

Storm-3168 dùng service principal bị chiếm quyền để tấn công Azure
"Microsoft reported Storm-3168 (also tracked as JADEPUFFER) conducting Azure-focused attacks using compromised service principals, including reconnaissance, credential collection, and bulk destructive operations across storage accounts, SQL databases, Key Vaults, Function Apps, virtual machines, and App Services. The activity showed a rapid transition from discovery to deletion attempts, with many storage accounts successfully deleted while resource locks and storage-level deletion protections blocked some actions; recommended mitigations include protecting workload identities, enforcing least privilege, safeguarding recovery resources, and enabling Microsoft Defender for Cloud protections."
Rủi ro cao do service principal bị chiếm quyền có thể dẫn đến xóa dữ liệu hàng loạt và thu thập thông tin xác thực; các cơ chế như resource locks vẫn có giá trị giảm thiểu.
Có thể gây gián đoạn dịch vụ, mất dữ liệu và phát sinh chi phí khôi phục; môi trường Azure có quyền quá rộng sẽ chịu tác động lớn hơn.
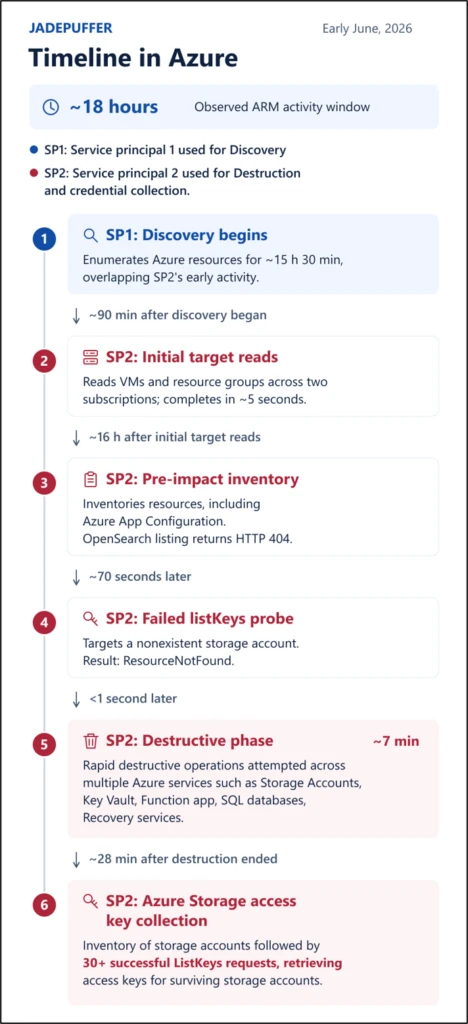
Microsoft ghi nhận hoạt động độc hại của Storm-3168 (còn theo dõi là JADEPUFFER) nhắm vào Azure bằng các service principal bị chiếm quyền. Nhóm này thực hiện trinh sát, thu thập thông tin xác thực và sau đó chuyển rất nhanh sang các hành động phá hoại trên Storage Accounts, SQL databases, Key Vaults, Function Apps, Virtual Machines và App Services.
Trong một tenant bị ảnh hưởng, một service principal đã thực hiện hơn 300 lượt đọc trong khoảng 15 giờ 30 phút để liệt kê tài nguyên. Một service principal khác chỉ mất 5 giây để quét máy ảo và resource group trên hai subscription, sau đó tiếp tục tìm cấu hình App Service và thử truy vấn Key Vault. Chưa đầy 7 phút sau chuỗi trinh sát, đối tượng này bắt đầu phá hoại, với hơn 150 thao tác liên quan đến xóa hoặc thu thập thông tin.
Nhiều Azure Storage accounts đã bị xóa thành công, nhưng resource locks và storage-level deletion protection đã chặn một số nỗ lực. Tổ chức nên bảo vệ workload identities, áp dụng least privilege, bảo vệ tài nguyên khôi phục, xoay vòng hoặc thu hồi credentials bị lộ và bật các biện pháp bảo vệ của Microsoft Defender for Cloud.